


Bank of America Hired 1,000 for Mythos Patches. Houston Businesses Need a Plan
Patch Management For Houston Businesses After Anthropic’s Mythos – A Five-Step Patch Backlog Plan For Houston Companies Without IT Staff
The bank bought patching capacity with contractors. A 10-to-200-person Houston business has to buy it with order.
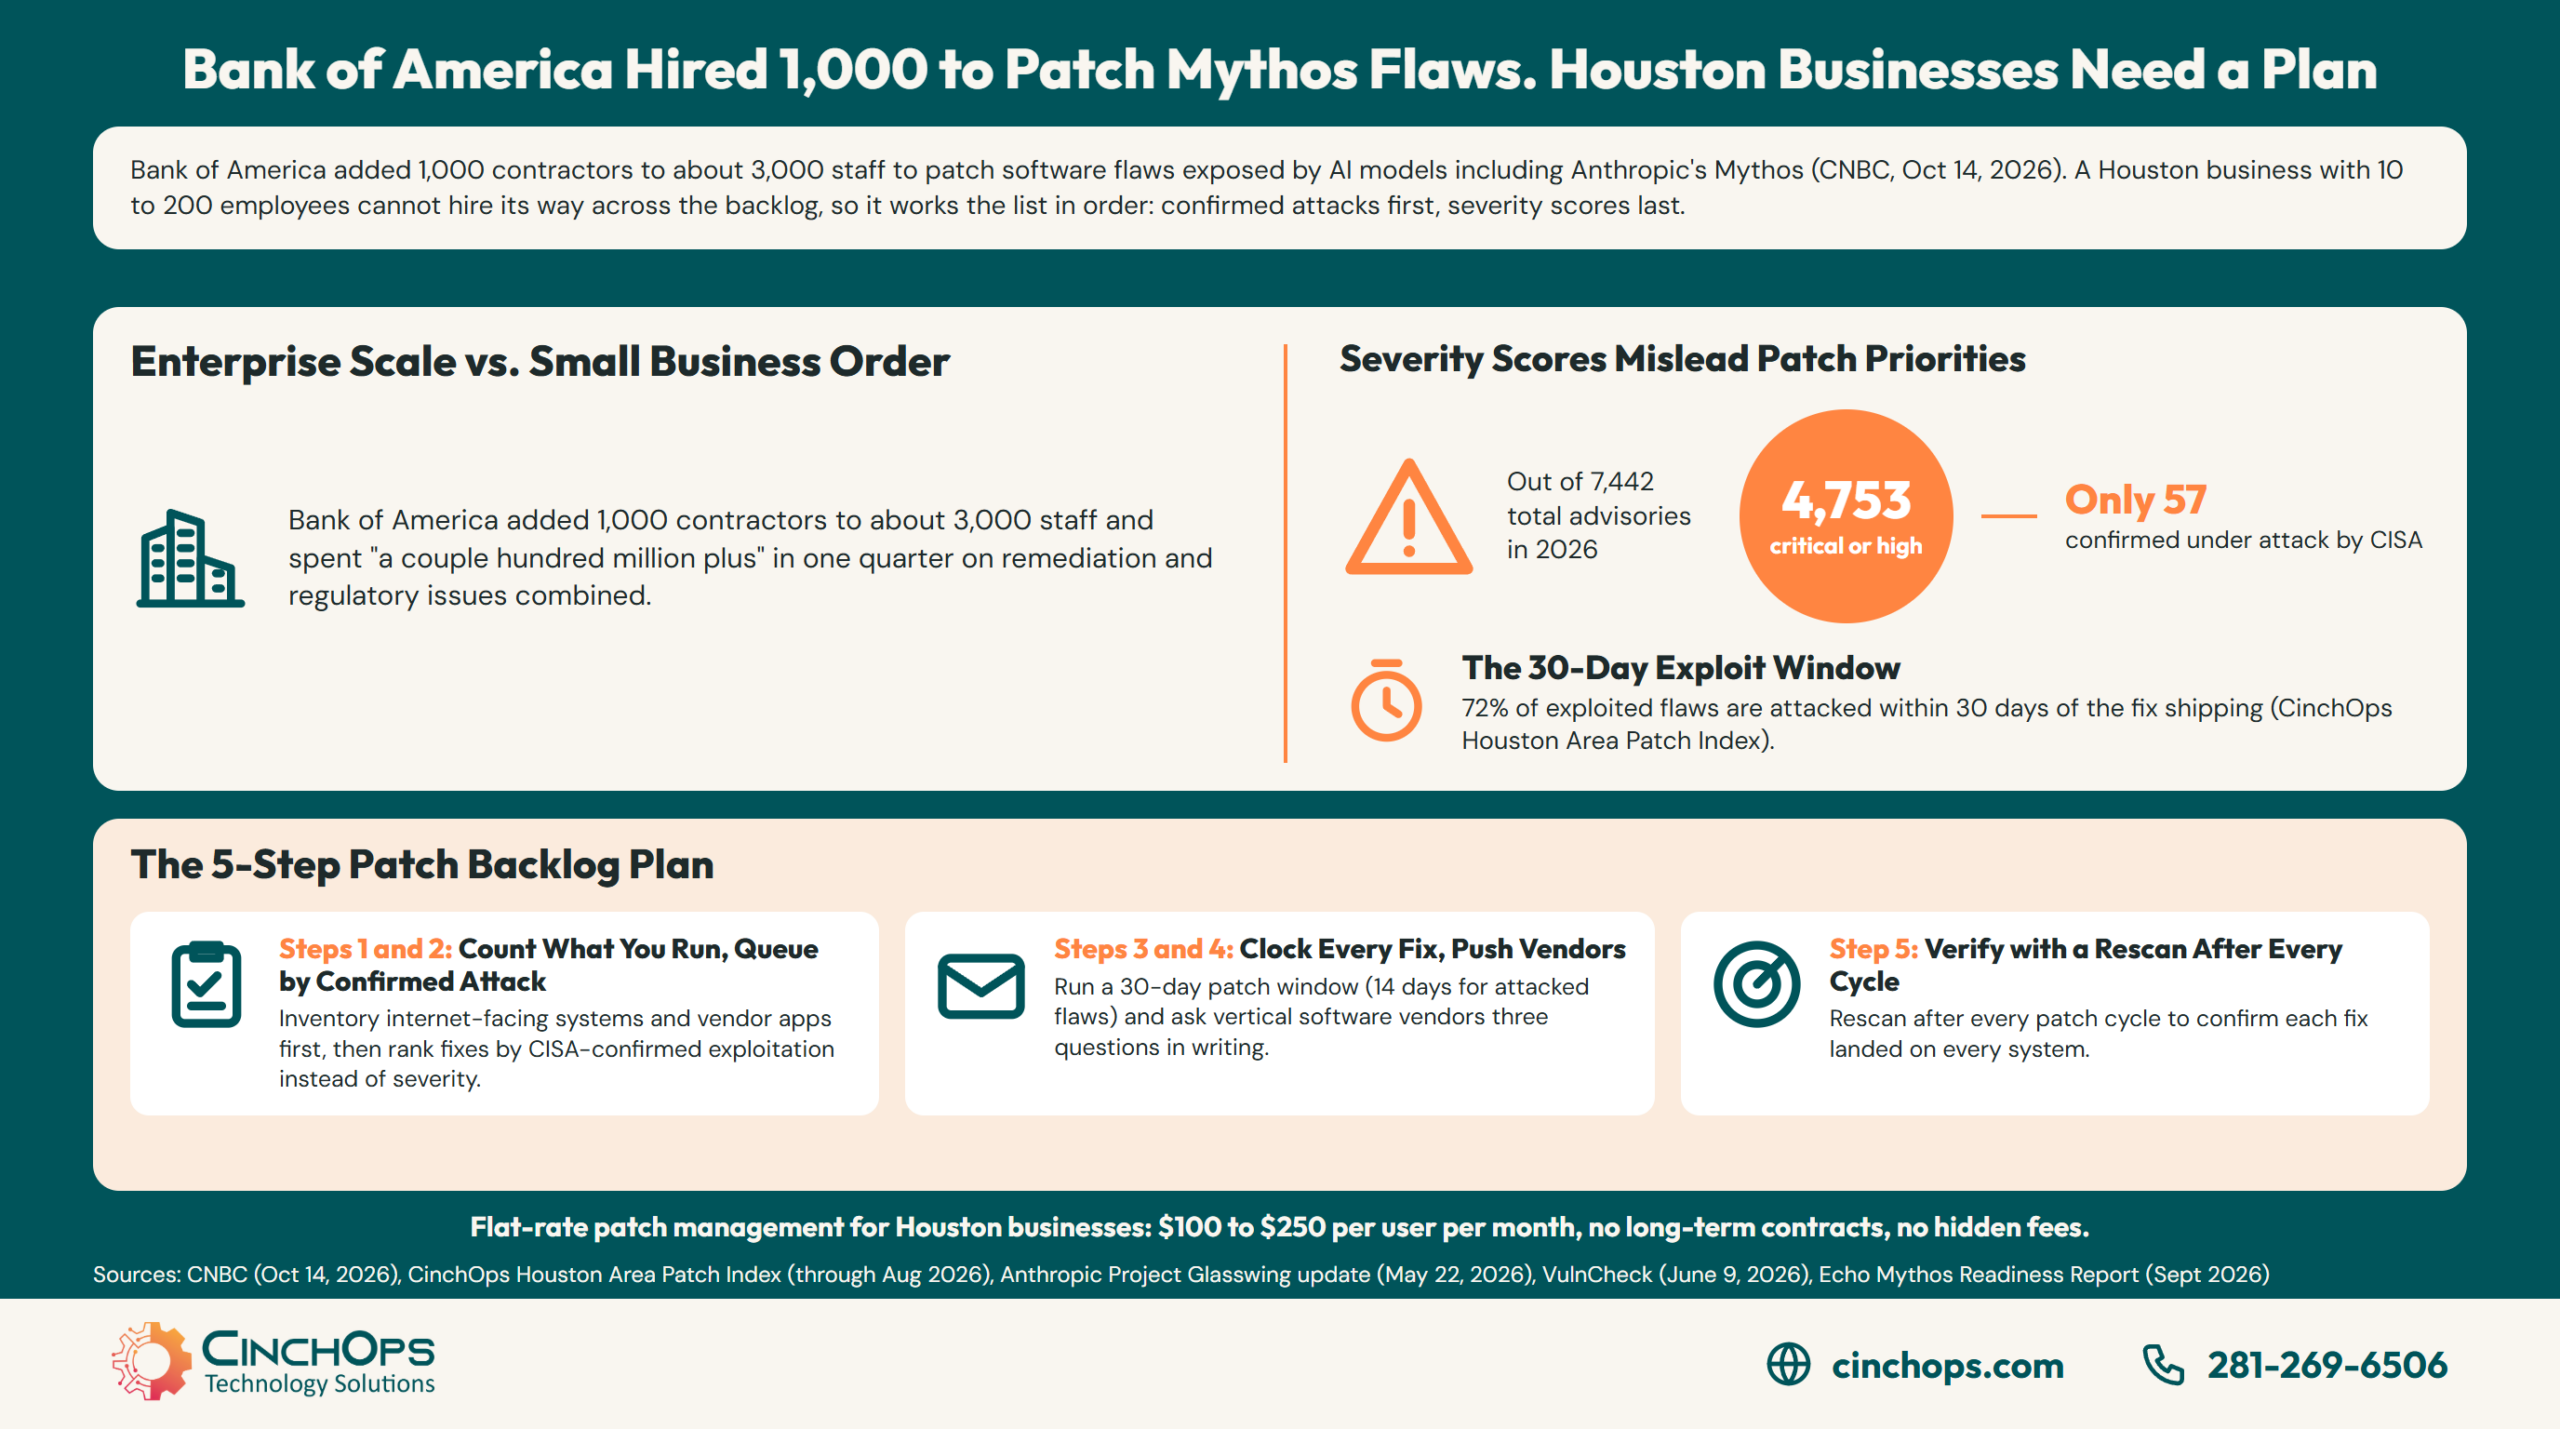
Bank of America's CEO told CNBC on October 14, 2026 that the bank put 1,000 contractors on patching work in the second quarter, on top of about 3,000 existing staff, to fix proprietary and vendor software flaws that AI models including Anthropic's Mythos had exposed. Read that as a Houston business owner and the Mythos patch backlog stops being a Wall Street story. The bank bought capacity. You do not have 3,000 people to add 1,000 to.
The same CNBC report puts the third-quarter bill for software remediation and anti-money-laundering regulatory issues, lumped together, at "a couple hundred million plus," and notes Bank of America shares fell as much as 8% that day. Moynihan also expects the cost to decline, because "once you patch, you don't have to patch as much." That last line is the useful one. The backlog is a one-time climb if you work it in the right order, and a permanent tax if you work it by headline.
CinchOps runs patch management specifically for 10-to-200-employee businesses across Houston, with a help desk that answers in under 15 minutes and a flat rate of $100 to $250 per user per month. The five steps below are the order that work runs in when a company has no patching staff of its own.
Step 1: Count What You Run Before You Count Patches
Bank of America's number only makes sense against the size of its software estate. Yours needs the same denominator.
A patch backlog is the list of fixes already published for software a business runs that have not yet been applied. Bank of America needed 4,000 people on that list, about 3,000 staff plus the 1,000 contractors Moynihan said were added in the second quarter and "remain here today." A 50-person Houston business has the owner, maybe an office manager, and whoever the managed IT provider assigns.
The capacity gap is not the point. The bank's estate runs to thousands of proprietary and vendor applications, which is why its CEO called the exposed vulnerabilities a "real risk" and spent a quarter's worth of nine-figure money on it alongside a separate regulatory cleanup. A Houston engineering firm with 60 staff runs perhaps 30 to 40 applications that matter, and a handful of them face the internet. The list is small enough to count by hand, and almost nobody has.
Start with four columns: the system, whether it is reachable from the internet, who patches it (you, your MSP, or the vendor), and the date it was last updated. Firewalls, VPN appliances, remote desktop gateways, the email server if one is still on premises, and any customer-facing web portal go first. Workstations and line-of-business software follow. The column that matters most is the third one, because everything in the vendor column is a patch you cannot apply yourself.
Moynihan's "once you patch, you don't have to patch as much" holds for a small business too, with one condition. The count has to be complete. A fix applied to 38 of 40 systems leaves the two the inventory missed, and those two are usually the old ones nobody wanted to own.
Step 2: Queue by Confirmed Attack, Not by Severity Score
The severity label on an advisory is the wrong sort key, and the Mythos data makes that measurable.
Severity describes what a flaw could do. Exploitation describes what attackers are doing with it. The CinchOps Houston Area Patch Index, built from 38,446 vendor advisories, found that of the 7,442 advisories published across tracked vendors in 2026, 4,753 were rated critical or high but only 57 had been confirmed under active attack by CISA. A queue sorted by severity puts 4,753 items ahead of the 57 that matter.
Mythos sharpens the problem in two directions. Anthropic's May 22 Glasswing update reported more than ten thousand high- or critical-severity vulnerabilities found by partners in the program's first month, so the flaw count is climbing faster than any patching team. At the same time, VulnCheck's June 9 read of Anthropic's disclosure ledger found that "Claude overestimated the severity of vulnerabilities it discovered compared to third party manual assessments." Echo's Mythos Readiness Report checked 27 public Mythos CVEs and found 14 of the model's ratings did not match the independent score, 13 of them rated too high.
So the severity column on an AI-found advisory is a draft. The confirmed-exploitation column is a fact. For a Houston business that means the queue is short: anything on CISA's known-exploited list that touches your inventory goes first, then internet-facing systems with a published fix, then everything else on a schedule. A law firm in Sugar Land does not need to patch 4,753 things this quarter. It needs the handful attackers are using, applied this week.
The order matters more for a small company than for the bank, because the bank can afford to work both lists at once. A 10-to-200-person business working the severity list first will still be on it when the next exploited flaw ships.
Step 3: Put a 30-Day Clock on Every Fix That Ships
Three published timelines set the pace a Houston business has to match.
A patch window is the time a business allows between a vendor shipping a fix and that fix being applied. The Houston Area Patch Index measured the gap between a fix's publication and CISA confirming exploitation across 353 cases: 72% of the flaws that get exploited were under confirmed attack within 30 days of the fix shipping, and 95% within a year. Thirty days is therefore the outer edge of a safe window, and the attacked list needs something closer to 14.
Anthropic's own figure points the same way. The May 22 Glasswing update said "on average, a high- or critical-severity bug found by Mythos Preview takes two weeks to patch" once it reaches a maintainer. VulnCheck's ledger read supplies the other side of the ledger: 23,019 candidate findings, 88 published advisories, "only 27 fixed findings," and at the observed pace "approximately 2.4 years to work through the backlog." Two weeks for the fix. Years for the queue. That gap is the backlog Bank of America paid contractors to close.
A Houston business cannot hire its way across it, so it schedules its way across it. Monthly patch cycles for workstations and servers, a 14-day pull-forward for anything on the exploited list, and an emergency window for internet-facing systems the day a fix lands. Echo's readiness report found 89% of CVEs already have a fix available, which means the schedule, not the vendor, is usually what is late.
Write the window down and put a name next to it. A clock nobody owns is the same as no clock, which is how most small-business backlogs got to be backlogs in the first place.
Step 4: Push Your Software Vendors, Then Verify the Fix Landed
Houston's industry mix puts an unusual share of the backlog in software the business cannot patch itself.
Vendor-managed software is any application whose updates are built and released by the vendor rather than applied by the business, and in Houston it carries more of the risk than in most markets. A Katy construction firm lives in Procore and Bluebeam. An oil and gas operator in the Energy Corridor runs WellView or P2 on top of its accounting stack. A CPA practice in Cypress sits inside CCH Axcess or Lacerte from January to April. Bank of America's contractors were patching "proprietary and vendor software," and the vendor half of that sentence is the half a small business shares with the bank.
Anthropic's Glasswing page says Mythos Preview "has already found thousands of high-severity vulnerabilities, including some in every major operating system and web browser," that Anthropic does "not plan to make Claude Mythos Preview generally available," and that details for many findings will be published only after fixes are in place. Your vertical software vendor is somewhere in that pipeline or outside it. Either way you can ask three questions in writing: whether the vendor has received Mythos-era findings, what has been fixed and when, and what the release schedule is for the rest. A vendor that cannot answer has told you where it sits.
Gulf Coast energy adds one more column. The UK AI Security Institute's April 13 evaluation found Mythos Preview "could not complete our operational technology focused cyber range," getting stuck on the IT sections of that range. Translation for a Houston operator: the model is strongest on the corporate side of the network, which is why IT/OT segmentation at the boundary between shop floor and corporate network is the control that keeps a corporate patch backlog from becoming a control-system incident.
Then verify. A patch that was approved, scheduled and reported as installed has not necessarily landed. Rescan after every cycle, and treat a system that still shows the flaw as a ticket, not a rounding error. Moynihan's "remain here today" is the bank admitting the second quarter's work was not finished in the second quarter. The verification scan is how a smaller company finds that out before an attacker does.
Which of your 40 systems is on the exploited list right now?
CinchOps builds the inventory, runs the queue and owns the 30-day clock for Houston businesses with no patching staff.
Talk to CinchOpsBank of America could afford to hire 1,000 people and work the whole list. A 50-person company in Katy gets one list and has to work it in the right order, which means the exploited flaws first and the severity scores last.
Patch management that runs on exploitation data, not advisory counts
CinchOps patch management sorts every Houston client's queue against CISA's exploited list and the Houston Area Patch Index, applies fixes on a written window, and rescans to confirm they landed. Monitoring runs 24/7; the help desk answers in under 15 minutes during business hours.
See how CinchOps patches what matters →How CinchOps Can Help Houston Businesses Work the Mythos Patch Backlog
CinchOps is a managed IT services provider based in Katy, Texas, serving small and mid-sized businesses across the Houston metro area. CinchOps specializes in cybersecurity, network security, managed IT support, VoIP, and SD-WAN for businesses with 10 to 200 employees.
The five steps above are the service, in order. CinchOps counts the estate during onboarding, queues it against confirmed exploitation, runs the patch window on a schedule with a named engineer who knows the network, chases vertical software vendors for their release dates, and rescans after every cycle. Pricing is a flat monthly rate per user, $100 to $250 per user per month, with no long-term contracts, no hidden fees and no cancellation penalties.
- Through patch management, the queue, the clock and the verification scan are owned by someone whose job it is.
- Through vulnerability scanning, the inventory in step 1 is built from what is actually reachable, not from what the business remembers buying.
- With cybersecurity services that include 24/7 threat monitoring, a flaw that gets exploited before its patch window closes is seen rather than discovered later.
- For oil and gas, manufacturing and energy services clients, IT/OT segmentation keeps the corporate backlog on the corporate side of the boundary.
- For construction, CPA firms and law firms, the vendor-column questions go out on the client's behalf and the answers go in the file.
- Service across Houston, Katy, Sugar Land, Cypress and The Woodlands.
Bank of America's backlog made the news because the bank could put a dollar figure and a headcount on it. Your backlog is smaller, unmeasured and usually sorted in the wrong order, which is the worse position of the two. Get the count done, put the exploited flaws at the top, and if you would rather someone else owned the clock, talk to CinchOps.
Frequently Asked Questions
Why did Bank of America hire 1,000 contractors to patch software?
CEO Brian Moynihan told CNBC on October 14, 2026 that Bank of America added 1,000 contractors in the second quarter, alongside about 3,000 existing staff, to patch proprietary and vendor software flaws that AI models including Anthropic's Mythos had exposed. He said the contractors remain on the job and called the vulnerabilities a real risk.
Does the Mythos patch backlog affect a small Houston business, or only banks?
It affects any business that runs software, because the flaws Mythos finds sit in operating systems, browsers and vendor applications everyone uses. Anthropic says Mythos Preview found flaws in every major operating system and web browser. A Houston business with 40 applications shares the vendor half of Bank of America's problem without the bank's staff.
Should a Houston business patch by severity score or by exploitation?
By exploitation. The CinchOps Houston Area Patch Index found that of 7,442 advisories published in 2026, 4,753 were rated critical or high but only 57 were confirmed under attack by CISA. VulnCheck also found Mythos overrated severity against manual review. The confirmed-exploitation list goes first, internet-facing fixes second, the rest on a schedule.
How fast does a Houston business need to apply a patch once it ships?
Inside 30 days for everything, and inside 14 days for anything on the exploited list. The Houston Area Patch Index measured 353 cases and found 72% of exploited flaws were under confirmed attack within 30 days of the fix shipping, and 95% within a year. Anthropic reports a Mythos-found bug averages two weeks to patch once a maintainer has it.
What does patch management cost in Houston?
Managed IT in Houston that includes patch management generally runs $100 to $250 per user per month. CinchOps prices patch management inside its flat per-user rate of $100 to $250 per user per month, with no long-term contracts, no hidden fees and no cancellation penalties, so a 50-person Houston business can budget the clock, the queue and the verification scan as one line.
What should a Houston business ask its software vendor about Mythos?
Three things, in writing: whether the vendor has received Mythos-era vulnerability findings, what has been fixed and on what date, and the release schedule for the rest. Anthropic publishes details only after fixes are in place, so a vendor that cannot answer is either outside the disclosure pipeline or behind on it. Either answer changes how the business plans.
Discover More
Resource
Sources
- CNBC, Hugh Son, "Bank of America hired 1,000 contractors to patch software flaws exposed by Anthropic's Mythos" (October 14, 2026)
- Anthropic, Project Glasswing (announced April 7, 2026)
- Anthropic, "Project Glasswing: An initial update" (May 22, 2026)
- VulnCheck, "Observations on Anthropic's Vulnerability Disclosure Ledger" (June 9, 2026)
- Echo, Mythos Readiness Report (September 3, 2026)
- UK AI Security Institute, "Our evaluation of Claude Mythos Preview's cyber capabilities" (April 13, 2026)
- CinchOps, Houston Area Patch Index (38,446 advisories; 2026 figures through August 2026)


