

9 Things to Do After Your Cyber Insurance Renewal Questionnaire Arrives
Building And Keeping A Cyber Insurance Answer Pack – What Houston Businesses Should Add To The Backup Answer
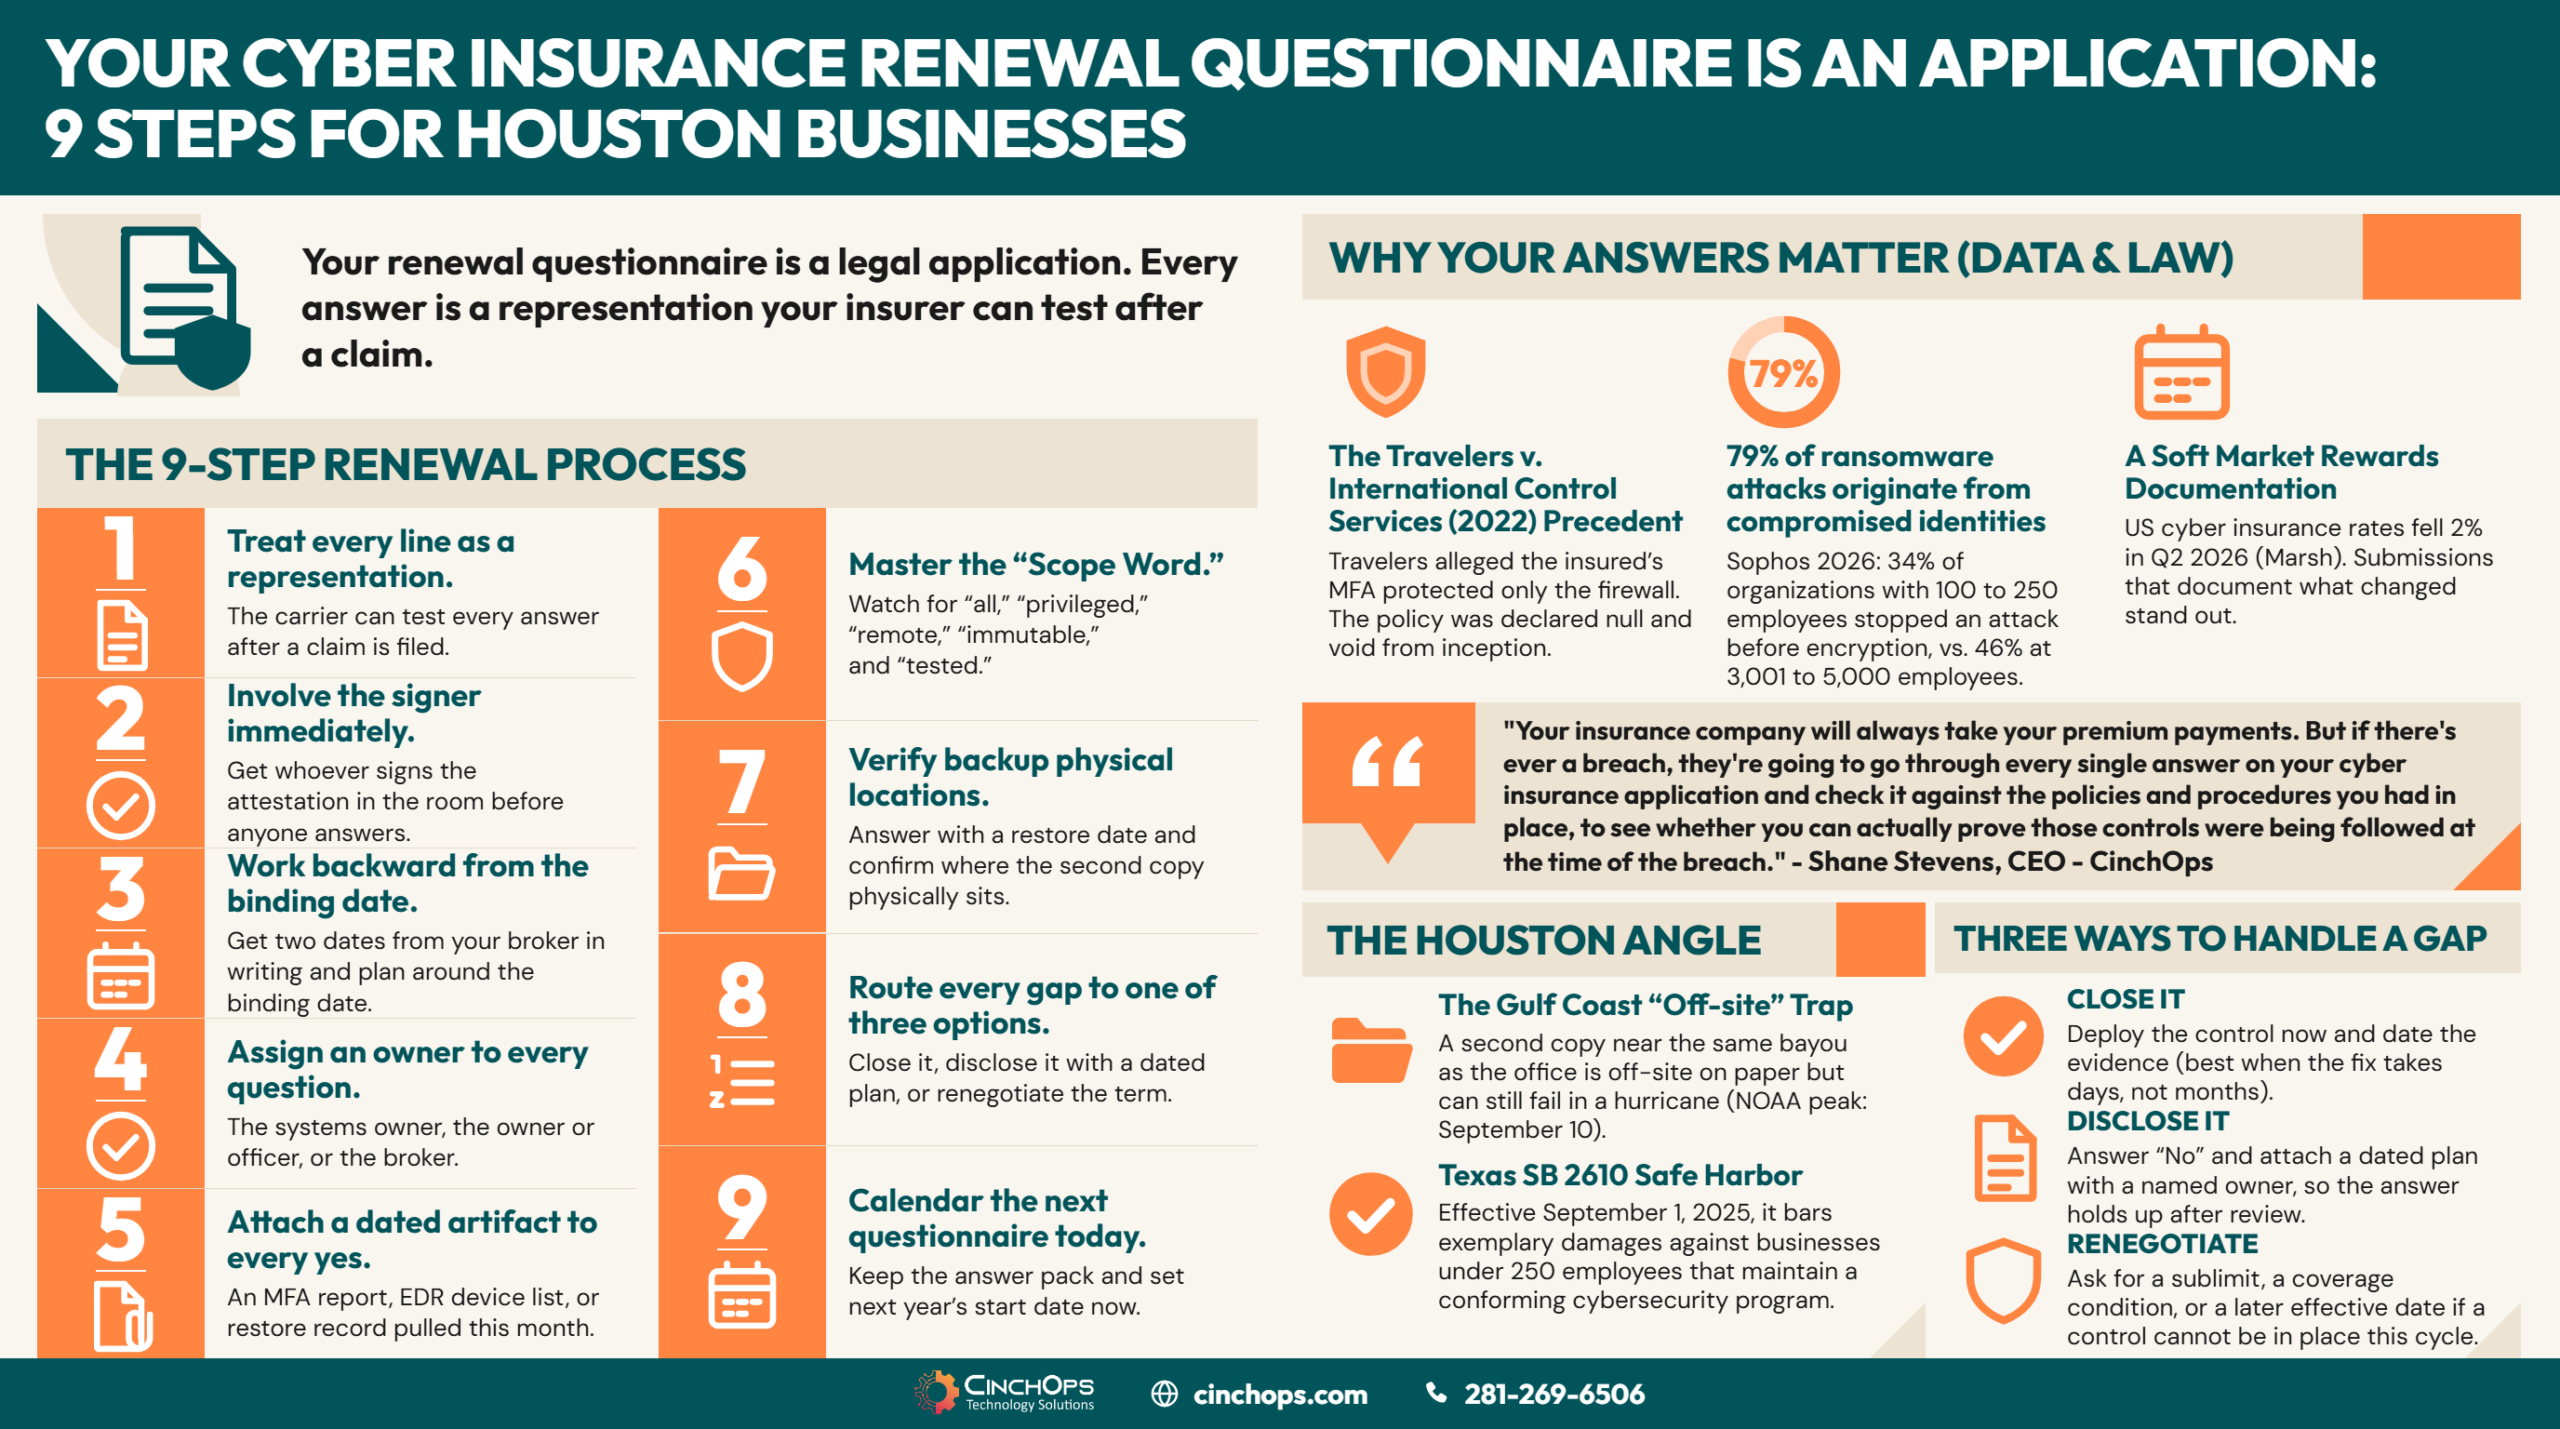
9 steps for Houston businesses, from the day the packet lands to the day you sign it.
A cyber insurance renewal questionnaire is an insurance application with a signature block, and every answer on it is a representation your carrier underwrites on. For a Houston business, that makes the two weeks after the packet arrives more consequential than the renewal date itself.
The packet lands in the inbox. Page three asks whether multi-factor authentication covers all remote access, whether endpoint detection and response runs on every device, and whether backups are immutable and tested. Most owners know roughly what the answer is. Almost none can prove it in an afternoon. CinchOps runs cyber insurance readiness for Houston-area businesses with 10 to 200 employees, assembling the MFA, EDR, and restore-test evidence a renewal questionnaire asks for at a flat monthly rate of $100 to $250 per user.
The order below matters more than the speed. Answering fast and answering provably are different projects, and only one of them holds up after a loss.
Read the Questionnaire as an Application Before You Answer a Line
Steps 1 and 2: what the document actually is, and who is legally on the hook for it.
A representation is a statement of fact an insurer relies on to decide whether to write a policy and at what price. If a representation on a cyber insurance renewal questionnaire turns out to be materially wrong, the carrier can ask a court to rescind the policy back to the day it started, which is a different and worse outcome than having one claim denied.
1. Treat every line as a representation the carrier can test after a claim
In July 2022 Travelers Property Casualty Company of America sued International Control Services in federal court in Illinois after a ransomware event at the manufacturer that May. Travelers alleged the company "only used MFA to protect its firewall, and did not use MFA to protect any other digital assets," while its application and a separate MFA attestation, signed that March, said otherwise. The policy had incepted on April 4, 2022. On August 26, 2022 the two sides jointly asked the court to declare the policy "null and void, from its inception," with no coverage available for past, present, or future claims. Each side paid its own costs.
Read that timeline again by the calendar. The application was signed in March, the policy started in April, the attack hit in May, and by late August there was no policy at all and never had been. The form, not the firewall, is what decided it.
Before anyone types an answer, write one sentence at the top of page one: every answer here is a fact we will have to prove to a forensic examiner. That single reframe changes how the technical questions get answered, and it is free.
2. Find out who signs the attestation, and get that person in the room first
Cyber applications usually carry two signatures: an officer of the company, and whoever is responsible for network and information security. In the Travelers filing, the application and the MFA attestation were both signed by the company president. If an IT provider fills in the technical lines and an owner signs the form without walking through them, the owner has just certified facts nobody compared notes on.
Put one 60-minute session on the calendar with three people in it: the owner or officer who will sign, the person who actually runs the network, and the broker on the phone. In onboarding audits we routinely find that the attested control set and the deployed control set are not the same document. It is almost never dishonesty. It is that the person who knows the network and the person who signs the form have never sat down together.
Work Backward From the Binding Date, Not the Renewal Date
Steps 3 and 4: the deadline that actually governs, and how to split the form so nobody answers someone else's column.
The renewal date is when coverage changes. The binding date is when the underwriter needs a complete submission in hand to quote it, and it sits earlier. Every deadline on a cyber insurance renewal questionnaire should be counted backward from the binding date, because that is the last moment a control you deploy this week can still show up in your pricing.
3. Get two dates from your broker in writing, and work backward from the second one
Ask for both: the date the broker needs the completed questionnaire, and the last date a changed answer can still affect the quote. Brokers will give you the first one unprompted and rarely volunteer the second. The second is the one that matters. It tells you whether a control you can stand up in 9 days is worth standing up now or worth scheduling for next quarter with a disclosure attached.
Write both dates at the top of the form next to your sentence about forensic examiners. Then count backward: evidence gathering, gap decisions, review session, signature. If that arithmetic does not fit, you have learned something useful on day one instead of day twenty.
4. Give every question an owner before anyone starts typing
Print the questionnaire and number every question. Then assign each one to a person. The questions sort into three columns, and nobody answers another person's column.
- The person who runs the systems takes MFA, EDR, patching, backup, email security, logging, and remote access.
- The owner or officer takes prior incidents and claims, revenue and record counts, funds-transfer procedures, vendor and client contract obligations, and anything asking what the business does.
- The broker takes policy structure: sublimits, waiting periods, prior-acts language, and what the last policy actually said.
The questions that sink a submission are usually not the technical ones. They are the business ones, and they get answered badly when whoever is holding the form guesses. A wire-transfer verification question answered by an IT technician who has never seen the accounting workflow is a representation with nobody behind it.
Every Yes on the Form Needs an Artifact Behind It
Steps 5, 6, and 7: the document that proves each answer, the qualifier that changes it, and the recovery questions a Gulf Coast business should answer twice.
An artifact is the export, report, or record that shows a control running, with a date on it. On a cyber insurance renewal questionnaire, a yes with no artifact behind it is not a yes yet, because the only version of that answer anyone will ever review is the one a forensic team reconstructs from the network after a claim.
5. Attach a dated artifact to every yes
Pull each one this month, not last year. Dates on the exports are part of the point.
- MFA coverage: the identity provider's per-user MFA or sign-in report showing enrollment and enforcement, plus a written count of every account excluded and why.
- EDR deployment: the security console's device list set next to the asset inventory, with the difference between the two numbers explained rather than ignored.
- Backups: the record of the last successful restore. What was restored, by whom, on what date, and how long it took.
- Patching: the patch report for the most recent full cycle, with named exceptions and the reason each one is excepted.
- Security awareness training: completion records with names and dates. A purchase receipt for a training platform is not a completion record.
- Incident response plan: the document itself, carrying a revision date and working phone numbers, plus the date it was last exercised.
- Email security: the tenant configuration export covering the specific settings the question names, not a general statement that the tenant is hardened.
Underwriters increasingly want to see this material rather than a checkbox. Broker Lockton's read on the Travelers case is that cyber applications have become longer and more complex, and that answering them takes real care and a thorough understanding of what is being asked. That is a polite way of saying the form is now the audit.
6. Read the scope word in every question, because that is where a true answer becomes a wrong one
The scope word is the qualifier that widens or narrows what is being asked: all, any, every, privileged, administrative, remote, external, company-owned, immutable, tested. Multi-factor authentication on a firewall is a true statement about a firewall. It is not an answer to a question that asked about administrative and privileged access to the network. That gap is the entire Travelers case.
- "All remote access" includes the vendor VPN, the ERP support tunnel, and the legacy RDP jump box somebody kept for one application.
- "All privileged accounts" includes service accounts, local administrator accounts nobody logs into, and the break-glass account in the safe.
- "Every endpoint" includes personal phones reading company mail, the shop-floor PC on an unsupported operating system, and the two laptops that live in trucks.
- "Immutable backups" means the copy cannot be altered or deleted inside the retention window by anyone, including your own domain administrator. A backup nobody has happened to delete is a different claim.
- "Tested" means a restore was performed and the restored data was verified. A backup job reporting success is not a test.
The identity questions carry the most weight in the file and the most exposure in the answer. Sophos' State of Ransomware 2026, a survey of 2,158 IT and security decision-makers across 17 countries, found 79% of ransomware attacks originate from compromised identities, and that only 34% of organizations with 100 to 250 employees stopped the attack before encryption or extortion, against 46% at 3,001 to 5,000 employees. Smaller companies get fewer chances to catch it, which is exactly why the underwriter is reading the MFA scope word closely.
7. Answer the recovery questions with a restore date and the second copy's address
The backup section usually asks three things: is there an off-site copy, is it immutable, and has it been tested. A Houston business should answer a fourth question the form does not ask. Where is the off-site copy, geographically?
A second copy sitting in a facility on the same bayou as the office satisfies the word off-site and fails the event. NOAA's National Hurricane Center puts the Atlantic peak at September 10, with most activity between mid-August and mid-October, which is the same stretch of calendar when a January renewal file gets assembled. CinchOps keeps client backups geo-redundant and stored outside the Gulf Coast flood zone, restore-tested on a schedule rather than assumed, because the questionnaire's definition of off-site and a storm's definition of off-site are not the same standard.
So answer with the date of the last verified restore, what was restored, and how long it took, then add where the second copy lives. A schedule is a plan. A restore date is evidence. From Katy to Sugar Land to Cypress, the businesses that answer this one cleanly are the ones that tested a restore in the spring rather than hoping in the fall.
Your insurance company will always take your premium payments. But if there's ever a breach, they're going to go through every single answer on your cyber insurance application and check it against the policies and procedures you had in place, to see whether you can actually prove those controls were being followed at the time of the breach.
What Do You Do About a Gap You Cannot Close in Time?
Step 8: three defensible routes for an answer you cannot truthfully give yet, and the fourth route that ends policies.
A gap on a cyber insurance renewal questionnaire has three honest exits: close the control now, disclose it with a dated remediation plan, or renegotiate the term with your broker. The fourth exit, answering yes and hoping nobody checks, is the one that produced a rescinded policy in the Travelers case and left a manufacturer with no coverage for its ransomware loss.
8. Route every remaining gap to close, disclose, or renegotiate, then tell the broker which
Close it when the fix is days rather than months: enforce MFA on the last exempted accounts, push EDR to the machines the console does not see, run the restore test. Deploy it, then date the evidence. The answer becomes a yes with an artifact behind it.
Disclose it when the work is real but lands after the binding date. Answer no, and attach a one-page plan naming the control, the person who owns it, and the completion date. A documented no reads very differently from a bare no, and unlike an optimistic yes it survives a forensic review.
Renegotiate when the control is not arriving this cycle at all. Ask the broker about a sublimit, a coverage condition, or a later effective date for that section. Coverage adjusts and the policy survives, which beats a policy that turns out to have never existed.
Then get the story in front of the person pricing it. Marsh's Global Insurance Market Index put US cyber insurance rates down 2% in Q2 2026 and global cyber rates down 4%, the 12th consecutive quarter of declines. A soft market does not reward a thin submission; it rewards the one that documents what changed. Send a single-page summary of what moved since last year with the artifacts attached, and confirm it reached the underwriter rather than stopping in the broker's inbox.
Would Your Answers Survive a Forensic Review?
CinchOps walks a cyber insurance renewal questionnaire with Houston-area businesses question by question, pulls the evidence behind every yes, and hands back the gaps in writing before anyone signs. Start with a cyber insurance readiness review.
See cyber insurance readiness →Keep the Answer Pack and Calendar the Next One
Step 9: the one action that makes next year's questionnaire a morning instead of a fire drill, and pays a second time under Texas law.
The answer pack is the folder of artifacts assembled to complete this cyber insurance renewal questionnaire, filed with a copy of the submitted form and the date it went out. Keeping it turns next year's renewal into a refresh instead of a rebuild, and it is the first thing a forensic team asks for if a claim ever lands.
9. File the answer pack and put next year's dates on the calendar the same day
Save the exports, the submitted questionnaire, the remediation plans, and the two dates the broker gave you, all in one place. Then open the calendar while the work is still fresh and set a reminder for 10 months out. Not for the renewal date. For the day you start the next one.
In Texas there is a second payoff for the same work. Senate Bill 2610, effective September 1, 2025, bars exemplary damages against a business with fewer than 250 employees that maintained a cybersecurity program conforming to a recognized framework. The statute scales with headcount: password policies and employee training under 20 employees, the CIS Controls Implementation Group 1 at 20 to 99, and a recognized framework such as NIST or the ISO/IEC 27000 series at 100 to 249. It does not touch compensatory damages or regulatory enforcement, so it is a partial shield rather than a blanket one. It is also built out of the same evidence the questionnaire just made you produce.
Ransomware is still what the underwriter is pricing. The Verizon 2026 Data Breach Investigations Report found 48% of breaches involve ransomware and 31% start with software vulnerabilities rather than stolen passwords. Those two numbers are why the patching questions sit right next to the identity questions on the form, and why the answer pack is worth keeping current between renewals rather than rebuilt under deadline.
How CinchOps Can Help Houston Businesses Answer a Cyber Insurance Renewal Questionnaire
CinchOps is a managed IT services provider based in Katy, Texas, serving small and mid-sized businesses across the Houston metro area. CinchOps specializes in cybersecurity, network security, managed IT support, VoIP, and SD-WAN for businesses with 10 to 200 employees.
- Through a cyber insurance readiness review, CinchOps works the questionnaire line by line, produces the artifact behind every yes, and returns the gaps in writing before the form is signed.
- Through cybersecurity services, CinchOps deploys and evidences MFA across privileged and remote access, EDR on every managed endpoint, email security, and awareness training with completion records.
- Through business continuity and disaster recovery, backups are geo-redundant, stored outside the Gulf Coast flood zone, and restore-tested on a schedule so the recovery answers carry a date instead of an intention.
- Through managed IT support, patching, access control, and documentation run as routine operations at a flat monthly rate per user, with no long-term contracts, no hidden fees, and no cancellation penalties.
- Across the service area, from Houston to Katy to Sugar Land, and for construction, CPA firms, and law firms whose clients increasingly ask the same questions the underwriter does.
The uncomfortable truth about a renewal questionnaire is that it is a better security audit than most businesses run on themselves, and it arrives with a deadline attached whether or not anyone is ready for it. Treat the packet as the audit rather than the paperwork, and the premium conversation takes care of itself. If the questionnaire is on your desk and you are not sure what the honest answer is on three of the lines, talk to CinchOps before you sign it rather than after.
Frequently Asked Questions
What is a cyber insurance renewal questionnaire?
A cyber insurance renewal questionnaire is the application a carrier uses to re-underwrite your policy. It asks line by line which security controls you run, and the answers are representations the insurer relies on. A materially wrong answer can let the carrier rescind the policy back to its start date.
Can a cyber insurance policy be voided because of a wrong questionnaire answer?
Yes. In July 2022 Travelers sued International Control Services after a ransomware loss, alleging the company used multi-factor authentication only on its firewall despite its application and MFA attestation. On August 26, 2022 the parties jointly asked the court to declare the policy null and void from its inception.
How long does it take to answer a cyber insurance renewal questionnaire?
Answering takes an afternoon. Proving the answers takes longer. Pulling MFA enforcement reports, EDR device lists, patch cycles, training completion records, and a verified restore is usually one to two weeks of real work for a business with 10 to 200 employees, which is why the packet should not sit unopened.
What should I do if I cannot put a control in place before the renewal date?
Answer no and attach a dated remediation plan naming the control, its owner, and the completion date. Then ask your broker about a sublimit, a coverage condition, or a later effective date. A documented no underwrites better than an optimistic yes, and it survives a forensic review after a claim.
Can an IT support provider in Houston handle the cyber insurance requirements section for me?
A provider can pull the evidence, close the gaps, and draft the technical answers, and cyber insurance requirements are standard work for a Houston managed IT support provider. The signature stays with you, so read what was written and confirm the scope words in each question match what is actually deployed.
What does cyber insurance readiness cost in Houston?
CinchOps prices managed IT and security work at a flat monthly rate per user, $100 to $250 per user per month depending on the tier, with no long-term contracts, no hidden fees, and no cancellation penalties. The controls a questionnaire asks about sit inside that rate rather than arriving as a separate project.
Discover More
Resource
Sources
- Insurance Journal, "Travelers Wants Out of Contract With Insured That Allegedly Misrepresented MFA Use," July 12, 2022
- Insurance Journal, "Travelers, Policyholder Agree to Void Current Cyber Policy," August 30, 2022
- Lockton, "Travelers v. ICS underscores need to respond carefully to cyber insurance application questions"
- Marsh, Global Insurance Market Index, Q2 2026
- Sophos, State of Ransomware 2026
- Verizon, 2026 Data Breach Investigations Report
- NOAA National Hurricane Center, Tropical Cyclone Climatology
- Texas Senate Bill 2610 (89R), enrolled text


