


Houston Area Patch Index: A Record October, With Attacks at the Edge
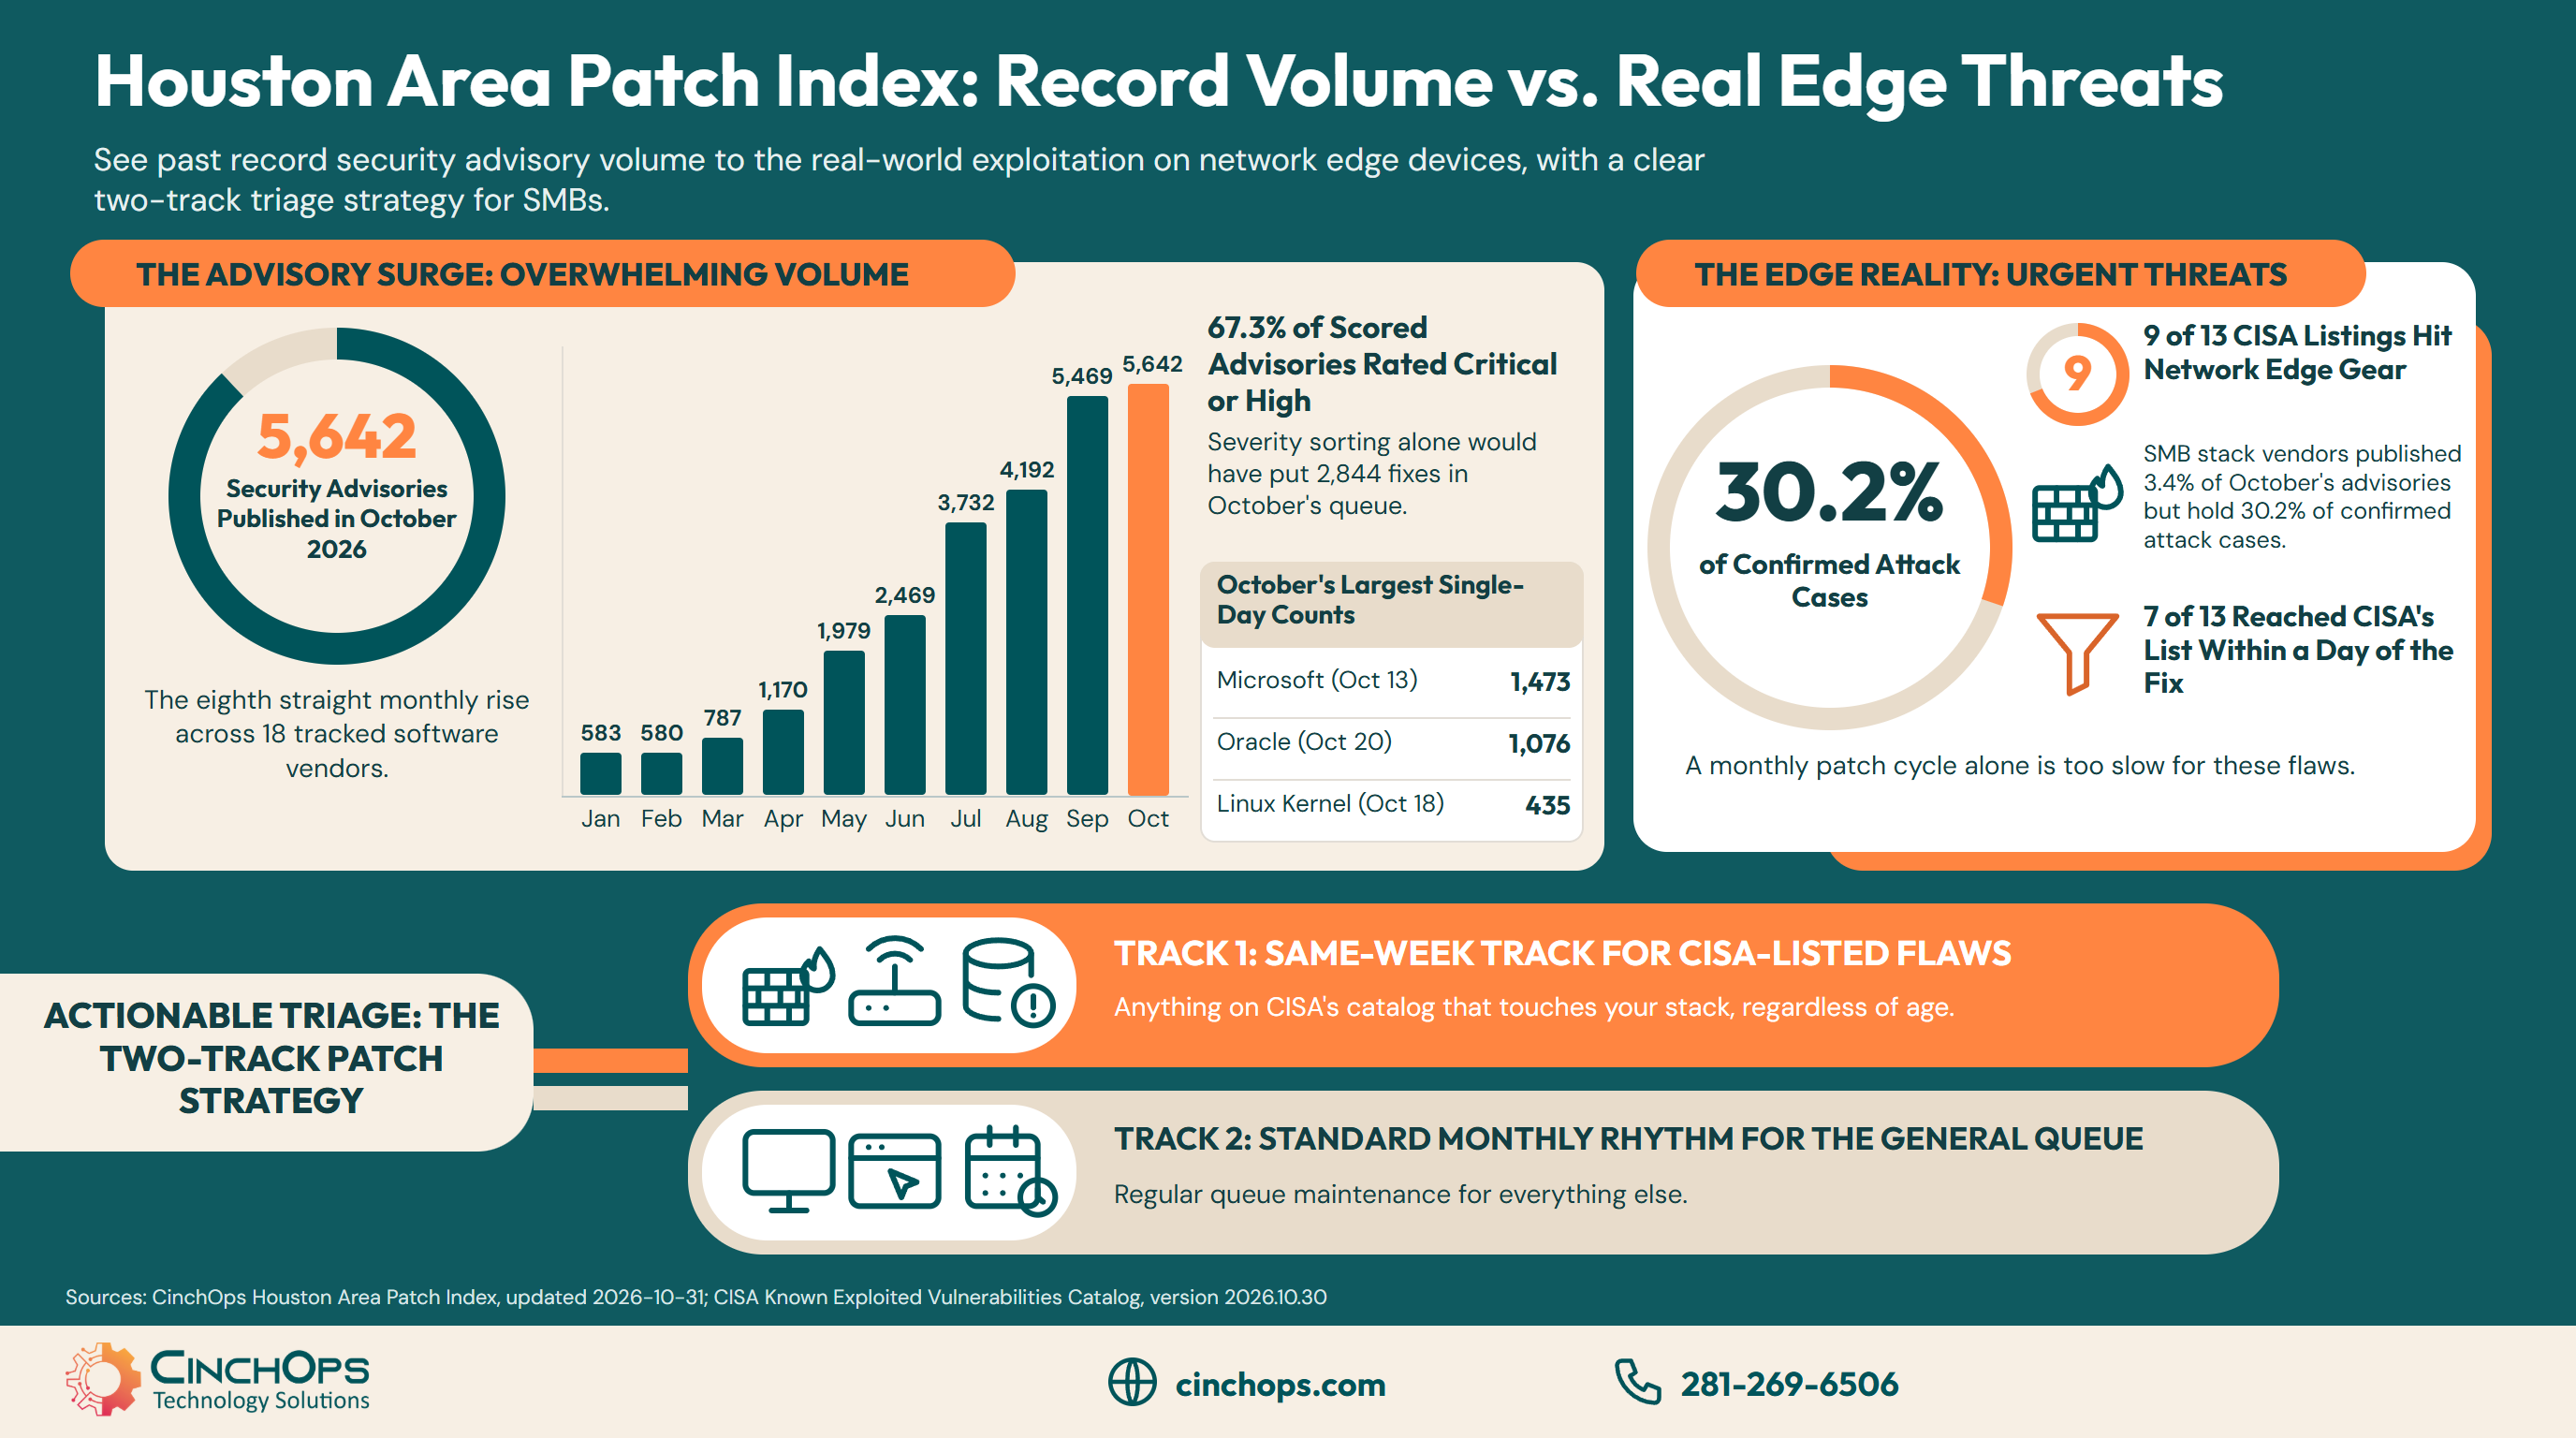
5,642 Security Advisories In October, A Record For The Index – Microsoft Shipped 1,473 Advisories In One Day
Vendors published 5,642 security advisories in October. CISA's exploited list points Houston businesses at a far shorter job.
The Houston Area Patch Index October 2026 refresh counts 5,642 security advisories from 18 software vendors through October 30, the most of any month since the index began in January 2022. September held the old record at 5,469, and the count has now risen for eight straight months. The Linux kernel accounts for August's increase: without it, August dipped from 2,897 to 2,549.
If you run a Houston or Katy business with a small IT team, another record patch month probably reads like another bill you can't pay in full. The useful question is which few fixes go first. This update answers it with October's data, then walks through the report page so you can run the same check against your own technology.
CinchOps provides managed IT and patch management specifically for small and mid-sized businesses in the Houston metro, using a public index of 54,209 advisories across 18 vendors to set patch priorities. The 2026 total stands at 26,603 advisories, a pace about 3.0 times 2025, and, with the Linux kernel left out of severity figures, the share rated critical or high climbed from 54.9% to 67.3%.
Microsoft, Oracle and Linux Drove the October Patch Record
Where the 5,642 advisories came from, and why a few release days account for most of them.
The October 2026 patch record belongs to three sources: Microsoft with 1,473 advisories, Oracle with 1,078 and the Linux kernel with 1,051. Together they supplied 3,602 of the month's 5,642 advisories, or 63.8%, according to the Houston Area Patch Index, and Google Chrome added another 732 across the month.
Microsoft's October 13 release is the largest single Microsoft release in the index, at 8.2 times its pre-2026 record of 180. Of the 1,473 advisories, Microsoft rated 94 critical and 1,375 high. CISA listed exactly one of them as exploited on release day, a Windows command injection flaw, CVE-2026-96951, which Microsoft rated high.
Oracle's date needs its own place on the calendar. Its October 20 Critical Patch Update carried 1,076 advisories, and the month's Oracle count was led by JD Edwards EnterpriseOne Tools at 84, PeopleSoft PeopleTools at 83, MySQL Server at 78 and Java SE at 53. A Houston contractor or energy services firm running JD Edwards had a bigger week on October 20 than on Patch Tuesday.
Read the counts as workload, with one caution. An advisory is one published CVE, and a single update can fix many CVEs at once, so 1,473 advisories never meant 1,473 separate installs. The report page marks two AI vulnerability-discovery programs that went public in spring 2026, and it states plainly that the index does not claim either one caused the surge.
Sort by Severity and You Get 2,844 Top Priorities
Testing the most common triage rule in small business IT against one month of data.
Sorting October's advisories by severity produces 2,844 critical-or-high fixes, or 68.7% of those carrying a score, with the Linux kernel left out as it is across the index's severity totals. Sorting by confirmed attacks produces 13 entries from the same vendors on CISA's catalog, a list a small team can finish.
The CISA Known Exploited Vulnerabilities catalog is the federal government's free public list of flaws with evidence of real-world attacks. CISA added 36 entries in October, as of catalog version 2026.10.30, and 13 came from the 18 vendors the index tracks. One of those 13, a late-October Ivanti entry, is not yet in the index's own exploitation tally.
Severity did its job in part. Of the 12 listings with a public CVE record, 10 scored critical or high, including FortiMail and Cisco Secure Email Gateway at 9.8. The trouble is width: those 10 were buried in a pile of 2,844, and a team working that pile from the top has no way to tell them apart. Two more would have missed the pile altogether, a Fortinet flaw scored 5.4 and a VMware ESX flaw scored 2.7.
Check the entire catalog against your inventory, because the other 23 October additions came from products outside the index. They include BeyondTrust Remote Support, Arista VeloCloud Orchestrator, Ahsay backup software and Plex Media Server. The index measures vendor workload, while the catalog is the working list.
Nine of the 13 Exploited Flaws Hit Firewalls, VPNs and Email Gateways
The original cut in this update: how little of the volume, and how much of the attack list, came from edge vendors.
Nine of October's 13 listings from tracked vendors hit network-edge products: Fortinet twice, Ivanti Connect Secure three times, Cisco twice, Citrix NetScaler and Palo Alto PAN-OS. The seven vendors the index groups as the SMB stack published 191 of October's 5,642 advisories, just 3.4% of the volume, for 69% of those listings.
One month is a small sample, so test it against the full record. Those seven vendors account for 3.7% of 2026 advisories (986 of 26,603) and 30.2% of every confirmed attack case in the index (134 of 443). Attackers keep returning to this equipment for a simple reason: it faces the internet by design, and it sits in front of everything else you own.
Here is the Houston problem. Firmware on a firewall or VPN appliance does not arrive through Windows Update, so a dashboard showing every laptop current can say nothing about the device most exposed to attack. A Houston-area firm with a Katy office, a Sugar Land site and crews in the field usually reaches its files through exactly this gear, and that makes the VPN a business-continuity dependency as well as a security one.
Energy, oil and gas, and manufacturing firms across the metro feel this most sharply. Process equipment often can't be rebooted on a Tuesday afternoon, so its real patch window stays long. The firewall or VPN standing in front of that equipment is usually the part that can move this week, and in October it was the part attackers were using.
No small business is going to patch everything, so the order is the whole job. If attackers are already using a flaw and you run that product, it goes first, this week, whatever its score says. Everything else waits its turn.
Exploited Flaws Move Faster Than a Monthly Patch Cycle
What October's listing dates say about a monthly patch cycle.
Six of October's 13 tracked-vendor listings reached CISA's catalog the same day their CVE record was published, and a seventh, Cisco's ASA and FTD flaw, arrived the next day. For those seven, attackers were already at work before a monthly patch cycle reached them, so a business needs a fast track.
That fits the longer record on the report page: across 405 confirmed cases, 70% of exploited flaws came under confirmed attack within 30 days of the advisory being published, and 95% within a year. A business patching monthly can be 30 days behind when those attacks land. A business patching quarterly can be behind on 82%.
The other end of the chart matters as much. Four listings were old fixes that CISA only added in October: VMware ESX at 90 days, Adobe Commerce at 105, the Linux kernel at 158 and a Fortinet flaw at 185. Any business that deferred those in the spring and forgot about them had an emergency arrive months later. One further Ivanti Connect Secure entry, CVE-2026-118527, had no public CVE record when checked on October 31, so its score and date are left out.
The working answer is two tracks. Keep the monthly rhythm for the general queue, and run a separate same-week track for anything CISA lists that touches your stack, old or new. Record what you defer and why, so a forgotten deferral can't turn into an October surprise.
Check Your Own Vendors in the Free Houston Area Patch Index
A top-to-bottom guide to the page, and how to use each part for your own business.
The Houston Area Patch Index report page is a free CinchOps tool that shows how much patching work 18 vendors generate, how severe it is and how fast attacks follow. It draws on CVE.org records, Microsoft's MSRC data and CISA's catalog, with no surveys, no self-reporting and no vendor participation.
- Headline numbers. Six figures at the top give the current scale: 54,209 advisories tracked, the 3.0 times pace, the 67.3% critical-or-high share, 26,603 in 2026, 5,642 in October and the 1,473 Microsoft release.
- Advisory Volume Over Time. This monthly chart filters by vendor group and switches between a combined total and one line per vendor. Dashed markers show when the two AI discovery programs went public and where Linux kernel records begin.
- Severity Mix by Year. This table shows critical, high, medium, low and unscored shares from 2022 through 2026, with the Linux kernel excluded.
- Build Your Stack. Select the vendors you run and the page calculates the load your team is absorbing. Start with your firewall vendor, since that's the one most owners forget.
- Vendor Detail. This sortable table gives each vendor's 2026 and 2025 counts, the change, confirmed attacks and the median days to CISA listing.
- Patch What Gets Attacked First. This section leaves out the Linux kernel and narrows 18,402 advisories in 2026 to 12,061 rated critical or high and 96 confirmed exploited, then gives four steps for a Houston business.
- Methodology and Revisions. These entries list the sources, the definition of an advisory, the known limitations and every dated data refresh.
Here is an example. A business running Microsoft, Fortinet and Veeam would see 4,434, 124 and 50 advisories so far in 2026, or 4,608 in total. The Vendor Detail table also shows how fast exploited flaws in each product tend to reach CISA's list: a median of 0 days for Microsoft, 4 for Fortinet and 40 for Veeam, which rests on a single case. Fortinet publishes about 3% as many advisories as Microsoft, yet its exploited flaws move almost as fast, so a small count is no reason to leave it for the monthly window.
Two limits are worth keeping in mind. The index does not grade vendors, because a high advisory count often reflects more transparency, while a vendor publishing none may simply have no disclosure program. And counts move as records change: September closed at 5,467 in the October 13 edition and reads 5,469 now. The data is free to reuse with credit and a link under the CinchOps Research Data Terms of Use.
Do You Know What Firmware Your Firewall Is Running?
If the answer takes more than a few minutes to find, October's list is the reason to fix that. CinchOps cybersecurity services prioritize fixes against the CISA catalog, so the flaws attackers are using jump the queue.
See how CinchOps handles it →How CinchOps Can Help Houston Businesses Act on the Patch Index
CinchOps is a managed IT services provider based in Katy, Texas, serving small and mid-sized businesses across the Houston metro area. CinchOps specializes in cybersecurity, network security, managed IT support, VoIP, and SD-WAN for businesses with 10 to 200 employees.
- Through managed IT support, CinchOps handles patch inventory, testing, deployment and verification at a flat rate of $100 to $250 per user per month, on Zero-Zero-Zero terms: no long-term contracts, no hidden fees, no cancellation penalties.
- Through cybersecurity services, fixes get ranked against the CISA catalog, and 24/7 threat monitoring watches for what patching hasn't reached yet. Help desk questions about a suspicious alert get an answer in under 15 minutes during office hours.
- Through business continuity and disaster recovery, backups stay geo-redundant outside the Gulf Coast flood zone, so a bad patch or a bad storm is a restore rather than a rebuild.
- CinchOps serves Houston, Katy, Sugar Land, The Woodlands and Cypress, with industry practices for energy services, oil and gas, manufacturing, construction and engineering firms.
November's count will probably be another large number, and it won't change what you should do on Monday. Know what sits at your network's edge, check it against CISA's list every week, and keep a record of what you defer. If nobody at your company owns that job today, talk to CinchOps.
Frequently Asked Questions
What is the Houston Area Patch Index?
The Houston Area Patch Index is a free CinchOps research page that tracks security advisories from 18 software vendors since January 2022, now 54,209 in total. It measures the patching workload those vendors create, how severe the flaws are, and how quickly CISA confirms attacks against them, using public data only.
How many security advisories were published in October 2026?
The Houston Area Patch Index counted 5,642 advisories in October 2026 through October 30, across 18 vendors. That beats September's 5,469, the previous record. Microsoft's October 13 release alone carried 1,473, and Oracle's October 20 update carried 1,076. The last day of October arrives with the next data refresh.
What is patch management and why does it matter?
Patch management is the routine of finding, testing, installing and confirming software fixes across a business. The Houston Area Patch Index shows why: 70% of exploited flaws come under confirmed attack within 30 days of the advisory being published. The fix usually exists already, so the exposure is the delay in applying it.
Which October flaws should a Houston business check first?
Start with CISA's Known Exploited Vulnerabilities catalog and match it against what you run. In October 2026, Fortinet, Citrix NetScaler, Ivanti Connect Secure, Cisco and Palo Alto Networks accounted for 9 of the 13 listings from the 18 tracked vendors. Firewalls, VPNs and email gateways therefore deserve the first look in most Houston offices.
What does patch management cost in Houston?
Managed IT that includes patching in Houston is typically priced per user per month. The published CinchOps rate is $100 to $250 per user per month, flat, with patch inventory, testing, deployment and verification included in managed IT, and with no long-term contracts, hidden fees or cancellation penalties under its Zero-Zero-Zero terms.
How often is the Houston Area Patch Index updated?
CinchOps has refreshed the Houston Area Patch Index five times since its August 2, 2026 publication, most recently on October 31, 2026, and each refresh is logged in the Revisions entry on the page. Counts can shift between editions as CVE records change, which is why September moved from 5,467 to 5,469.
Discover More
Resource
Sources

